THE recent shutdown of an illegal scam operation using fake base transceiver station devices has renewed warnings for the public to treat SMS messages with extreme caution, even when they appear to originate from trusted or familiar numbers, cybersecurity specialists said.
Cybersecurity expert Fong Choong Fook said fake BTS devices are designed to impersonate legitimate telecommunications towers, tricking nearby mobile phones into connecting to them without users’ knowledge.
“A BTS is essentially a base station that mimics the operation of a telecommunications company’s cell tower, but on a smaller scale. Think of it like a Wi-Fi hotspot,” he told The Star.
Fong explained that mobile phones are programmed to automatically connect to the strongest available signal, a vulnerability that scammers exploit by deploying fake BTS devices in crowded or high-traffic locations.
“Due to weaknesses in mobile phone protocols, phones tend to connect automatically to the strongest signal available. That’s why scammers place fake BTS devices in crowded or popular areas to target large groups of people,” he said.
Once connected, the rogue device allows scammers to send SMS messages directly to users’ phones, bypassing traditional network safeguards and enabling large-scale phishing attacks aimed at harvesting personal or financial information.
“These scams usually come in the form of SMS messages containing a web link. The public should remember that banks and telcos have been instructed not to include clickable URLs in SMS messages,” Fong said.
“As a general rule, if an SMS contains a link, there is a high chance it was sent by scammers. Do not click on it,” he added.
Fong said scammers commonly rely on fear and urgency to pressure victims, including messages warning that a WhatsApp account will be suspended or that urgent action is required to avoid financial or legal consequences.
He noted that while the misuse of fake BTS devices has existed for years, initially for aggressive location-based marketing, cybercriminals are now adapting the technology for more serious fraud.
“Today, cybercriminals are using the same technology for scams and fraud,” he said.
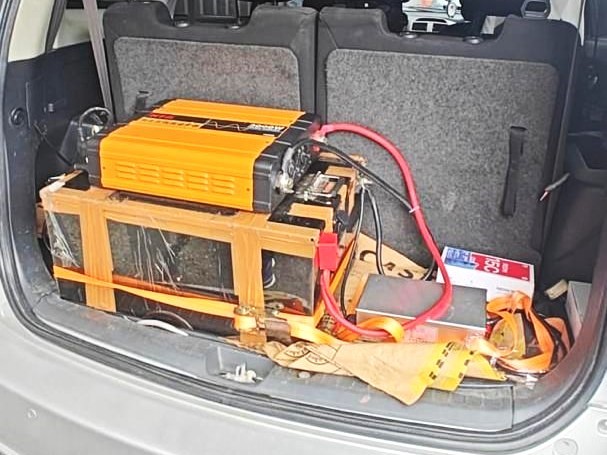
According to Fong, fake BTS equipment can be highly portable, with some units small enough to be hidden in a vehicle boot or installed discreetly in shop lots or on rooftops.
He said the recent operation by the Malaysian Communications and Multimedia Commission should be seen as part of sustained enforcement rather than an isolated case.
“MCMC continuously conducts BTS reconnaissance and scanning. Detecting and triangulating the location of a fake BTS is not easy. It requires coordination, technical capability and sustained effort,” he said.
Last week, MCMC announced it had successfully shut down a fake BTS operation in Genting Highlands, Pahang, following a joint operation with a telecommunications company. Two vehicles believed to have been used to transmit illegal signals were detected, suggesting a carefully planned effort to intercept networks and disseminate fraudulent SMS messages.
In a related development, fraud examiner specialist Raymon Ram said licensed financial institutions must strengthen internal SMS controls and reduce reliance on text messages for sensitive communications.
He said banks should enforce robust SMS policies, deploy secure multi-factor authentication, work closely with telecom authorities and actively educate customers about emerging threats.
While banks are responsible for securing their own messaging systems, Raymon said the underlying vulnerability lies in telecom infrastructure and protocols, where messages can be intercepted or manipulated before reaching recipients.
He cited a recent incident in which customers of a bank received SMS notifications from an official sender ID containing clickable links, a tactic used by scammers to gain credibility.
Although the messages were later removed and the issue addressed, Raymon cautioned against using SMS as a channel for critical actions.
“SMS should not be relied on for sensitive actions,” he said, noting that Bank Negara Malaysia has already mandated the gradual phasing out of SMS-based one-time passwords in favour of more secure alternatives such as mobile applications and hardware tokens.
“Banks must also implement fraud monitoring mechanisms that trigger rapid investigations when customers report suspicious messages. Cooperation with telcos and regulators, such as the MCMC, is essential,” he added. - February 6, 2026