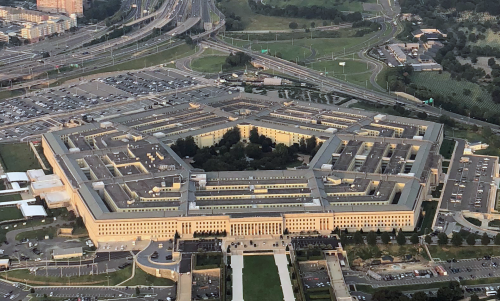

NEW YORK – The United States Department of Homeland Security (DHS) was the third federal department to be targeted in a major cyberattack, US media reported yesterday, a day after Washington revealed the hack which may have been coordinated by a foreign government.
The Washington Post cited unnamed officials who said that DHS – which is in charge of protecting the country from attacks both online and off – had been added to a growing list of targets in the attack, including the treasury and commerce departments.
A statement from DHS yesterday did not confirm the report, saying only that it was “aware of cyber breaches across the federal government and working closely with our partners in the public and private sector on the federal response”.
The Cybersecurity and Infrastructure Security Agency (Cisa), which is attached to DHS, said on Sunday that it had ordered federal agencies to immediately stop using SolarWinds Orion IT products following reports that hackers had used a recent update to gain access to internal communications.
“We urge all our partners – in the public and private sectors – to assess their exposure to this compromise and to secure their networks,” said Cisa acting director Brandon Wales.
SolarWinds over the weekend admitted that hackers had exploited a backdoor in an update of some of its software released between March and June.
The hacks are part of a wider campaign that also hit major cybersecurity firm FireEye, which said its own defenses had been breached by sophisticated attackers who stole tools used to test customers’ computer systems.
FireEye said it suspected the attack was state-sponsored, and warned it could have affected numerous high-profile targets across the globe.
“This campaign may have begun as early as Spring 2020 and is currently ongoing,” FireEye said in a blog post.
The content the hackers have sought to steal – and how successful they have been – is not known at this time.
“We believe this is nation-state activity at significant scale, aimed at both the government and private sector,” said IT giant Microsoft, which is also investigating, in a blog post.
While Microsoft refrained from naming a country, several US media pointed the finger at the Russian group “APT29”, also known as “Cozy Bear”.
According to the Washington Post, the group is part of Moscow’s intelligence services, and hacked servers at the State Department and the White House during the Obama administration.
The Russian embassy in the US categorically denied the accusations in a statement on Facebook.
Both the public and private sectors must be increasingly on guard against such hacks, warned Hank Schless, senior manager at Lookout, a California-based mobile security company.
“Adversarial nation-states have recognised the value in targeting both sectors, which means neither is safe from the types of attacks that have government resources behind them,” he said.
Matt Walmsley of Vectra, which provides cyberattack detection services from its base in California, agreed.
“Security teams need to drastically reduce the overall risk of a breach by gaining instant visibility and understanding of who and what is accessing data or changing configurations, regardless of how they are doing it, and from where,” he said. – AFP, December 15, 2020